
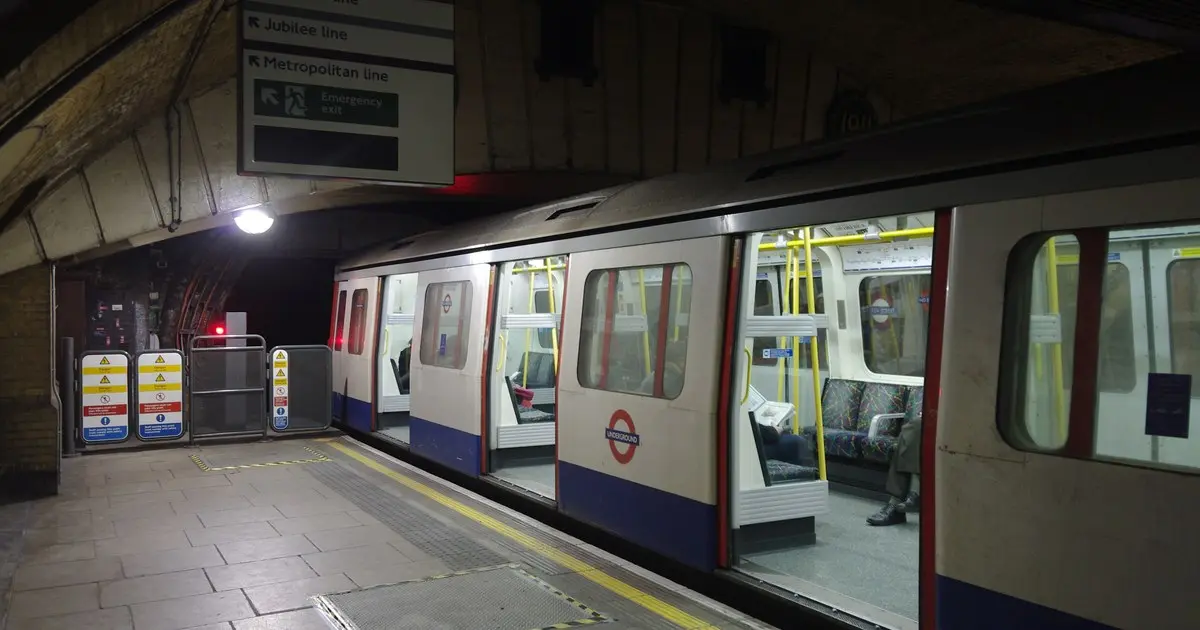
Transport for London has taken its Oyster photocard website offline after suspicious activity, with around 265,000 photocard customers told their account details may have been accessed.
The problem came to light on Monday, 16 November, when Oyster photocard customers began receiving emails asking them to create an account — even though they already had one.
TfL took the photocard website down straight away while the incident was investigated. It has now contained the incident and notified the Information Commissioner’s Office, the UK’s data protection regulator.
On Wednesday, TfL emailed some of those affected to say their name and contact details — including email address, phone number and home address — along with their date of birth and security question and answer, had been compromised.
Its current assessment is that no passwords, bank or payment card details, customer journey information, or the names and dates of birth of any children with a Zip Oyster card have been compromised.
Who is affected?
The customers who may have been affected hold one of these photocards:
- Zip Oyster cards (5-10, 11-15, 16+)
- 18+ Student Oyster card
- 18-25 Care Leaver Oyster photocard
- 60+ London Oyster photocard
- Apprentice Oyster photocard
- Veterans Oyster photocard
These are the discounted and concessionary travel cards that require a photocard and an online account, used by schoolchildren, students, older Londoners, apprentices and veterans, among others.
Shashi Verma, TfL’s director of technology strategy and revenue, said: “On 16 November 2026, we became aware that Oyster photocard customers were receiving emails asking them to create an account, when they already have a photocard account.
“We immediately took the TfL photocard website down while this was being investigated.
“The protection of personal information is a priority for us, and I apologise to our customers affected by this incident.
“While we acted swiftly, we now believe that around 265,000 photocard customers may have had their account details compromised as part of this incident.
“We have now contained the incident, and our current assessment is that no passwords, bank or payment card details, customer journey information, or names and date of births of any children with a Zip Oyster card have been compromised.
“Due to the speed with which this incident was identified and addressed, we believe that the number of customers who could have been affected was significantly reduced.
“We are continuing to investigate what has happened but have already contacted affected customers to make them aware of this.
“Customers with Oyster photocards can continue to travel and any customer who need to renew their photocard or query any journey history can still do so by contacting TfL’s Customer Services.
“We hope to restore the affected website services as quickly as possible.”
Can customers still travel?
Yes. People can continue to travel with their Oyster photocards and top them up through ticket vending machines in London Underground and National Rail stations. What they cannot do for now is access their online photocard accounts, because the website remains offline.
Anyone who needs to renew a photocard or query journey history can do so by contacting TfL’s Customer Services.
What should affected customers do?
Because names, addresses, phone numbers and dates of birth were among the details accessed, affected customers should be on their guard for phishing emails, texts and calls that use those personal details to look convincing.
TfL will never ask customers for passwords or bank details by email, and anyone contacted in that way should treat the message as suspicious.
Anyone who used the same security question and answer on other accounts should change it there too, since that combination is now in the hands of whoever accessed the photocard system.
TfL has said it has already contacted affected customers directly, so anyone holding one of the photocards listed above who has not heard from TfL should still keep an eye out for its message and for the website’s return.
A different incident from the 2024 cyberattack
This is a separate incident from the cyberattack on TfL in 2024, and the two should not be confused.
Between 31 August and 3 September 2024, hackers broke into TfL’s systems, rendering more than 140 systems inoperable and costing the transport network £29 million to put right. More than seven million customers were told their data may have been accessed.
Two members of the hacking group were sentenced at Woolwich Crown Court on 16 July 2026: Owen Flowers, 18, and Thalha Jubair, 19, each received five and a half years in prison after pleading guilty to hacking TfL.
That attack hit TfL’s wider systems, including Dial-a-Ride bookings and live travel information. This week’s incident is confined to the Oyster photocard website, which TfL took offline within hours of spotting the suspicious activity.
TfL says it is continuing to investigate what happened and will restore the photocard website as quickly as possible.